WordPress isn’t the only place people build websites anymore. AI builders and Node.js hosting are now standard offerings from our own hosting partners, and that shift has quietly recreated every security problem we spent five years solving in WordPress, just with a different tech stack.
Today we’re opening Early Access to Patchstack for Lovable, Replit, Base44, Claude Code, and other JS applications. It’s free during the early access period, after which standard pricing applies.
The same problem, a new ecosystem
AI-generated apps ship with more packages than the average WordPress site ships with plugins. Simple to-do apps ship with over 800 packages from the get-go, and the problem scales with complexity.
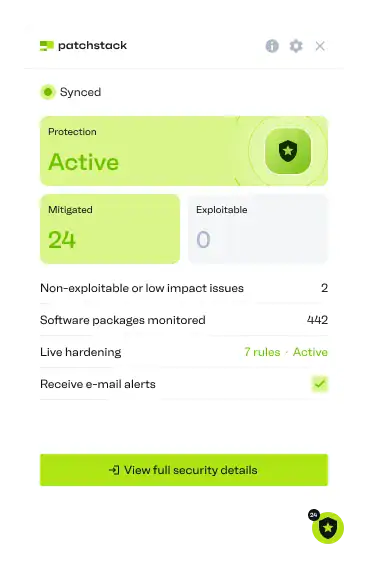
And once they’re live, most of these apps never get properly maintained. Even when a vulnerability is known, upgrading feels risky, so it doesn’t happen. That’s the same fear-of-breaking-things pattern that’s driven every major WordPress compromise we’ve mitigated.
The difference: the people building these apps skew less technical than WordPress developers, not more. A year ago, Node.js builders were mostly software engineers. Today they’re founders, marketers, and indie hackers who’ve never touched git. Most existing JavaScript security tools were built for the engineers who no longer represent the majority of the audience. They assume you can read a diff and patch code yourself. Most builders can’t, and most can’t afford enterprise tooling built for teams that can.
AI-assisted vulnerability research and AI-powered attacks make this gap more dangerous every month. And AI-generated patches don’t help if nobody applies them: rushing a package upgrade now carries its own risk of supply chain compromise.
How Patchstack secures your AI-built apps without touching your code
We’ve proven how well Patchstack works in WordPress. It works the same way here, deeper in the stack.
Patchstack RapidMitigate now runs inside the JavaScript application itself, identifying vulnerabilities, tracing their reachability, and mitigating them at application runtime.
When a new vulnerability surfaces, a mitigation rule deploys and activates automatically. No codebase changes. No rebuild. The vulnerability gets neutralized immediately, without exposing the app to a supply chain attack, and without the fear of an upgrade breaking something. You get time to patch properly, on your own schedule, with zero exposure in the meantime.
We’re also launching Live Hardening, a new output-filtering module in the same RapidMitigate runtime. Where mitigation stops incoming exploit attempts, Live Hardening watches what the app serves back out. It blocks Supabase secret key and service role key leaks, vendor API key and token leaks, private key leaks, and internal error messages that expose more than they should.
The entire process is simple: prompt to protect within your interface, and Patchstack will automatically install and start monitoring your apps.
One dashboard, every stack
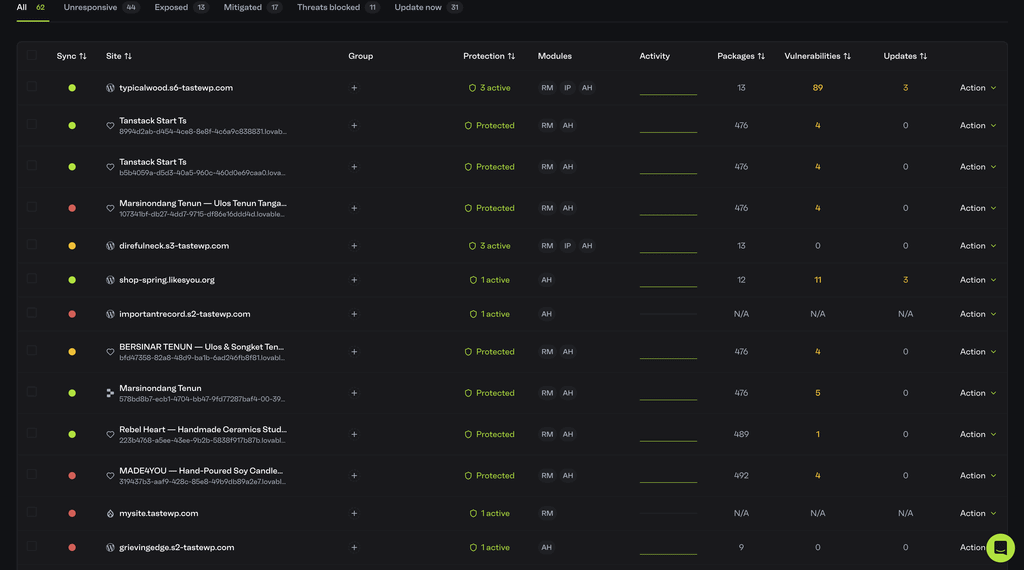
WordPress sites, AI platform apps, and custom Node.js apps hosted anywhere now live under one Patchstack account, with full visibility and control across all of them.
Security exactly where you build
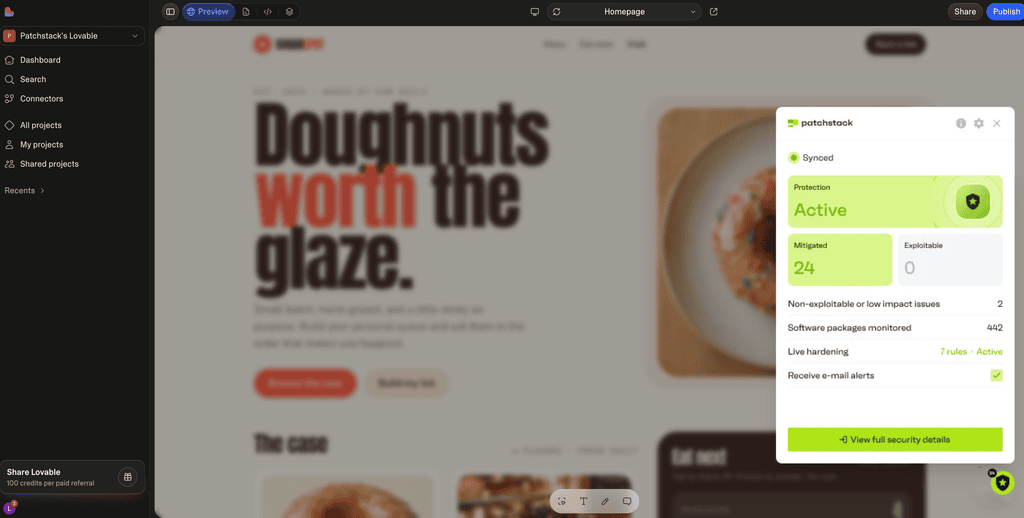
If you build primarily on platforms like Lovable, Patchstack’s quick access widget loads directly into your sandbox, putting the information and controls you need right where you’re already working.
Get Early Access
Early Access is live today, and it’s free. Standard SaaS pricing kicks in once the early access period ends. Request access here.