Introduction
Welcome back to our annual State of WordPress Security whitepaper. Another year has passed, and we are excited to share insights into the most notable security statistics and trends in the WordPress ecosystem observed in 2023.
This year, we’ve partnered with Sucuri. With both of our data combined, we can cover the entire timeline of security incidents from the vulnerability being found to the point where malware infection gets detected on a vulnerable website.
2023 was another record year of new vulnerabilities being discovered and fixed in the WordPress ecosystem. In 2023, we added 5,948 new vulnerabilities to the Patchstack vulnerability database. That’s 24% more than in 2022.
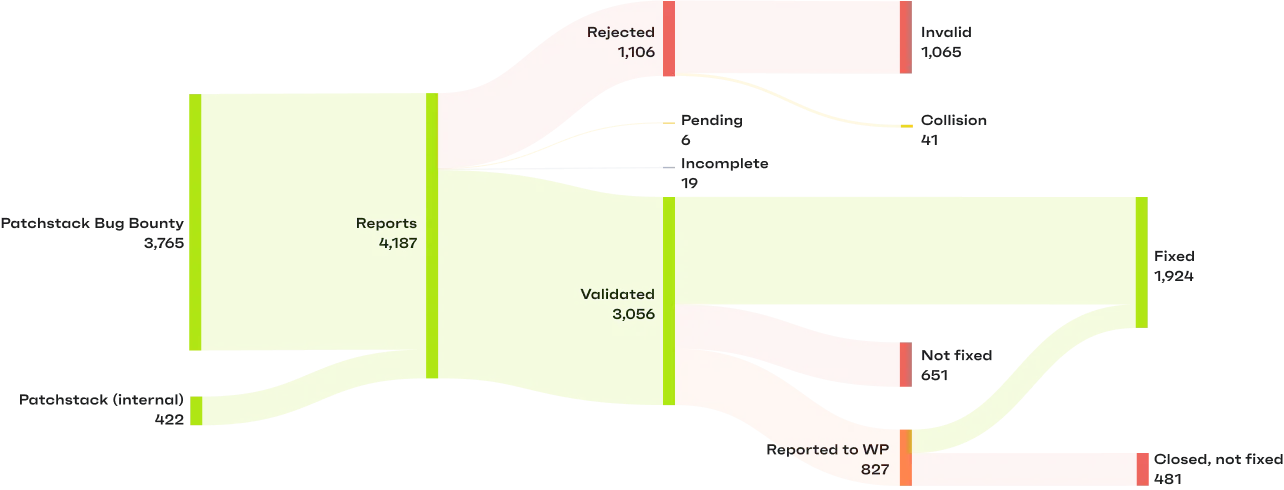
In 2023, our team reported 827 plugins and themes as abandoned to the WordPress team, a stark contrast from 2022 when we reported only 147 of such plugins. 58.16% were permanently removed from the plugin repository. It’s a sign of more and more plugins being abandoned, posing a huge security risk. However, the WordPress community’s security knowledge is growing, fueled by new regulations coming in 2024, including the new PCI DSS 4.0 standards for payment processing, EU’s Cyber Resilience Act, the US Securing Open-Source Software Act, and more. Developers and users are becoming increasingly tired of relying on “all-in-one solutions” propagating the endless loops of infections and cleanups.
The main keyword of 2023 WordPress security has certainly become: proactive, layered security.
Explore our Annual Security Report for a detailed look at key insights for plugin developers, WordPress website builders, and security experts.
About Patchstack
As the world’s #1 vulnerability processor (CNA) in 2023, Patchstack provides a vulnerability management and mitigation platform for WordPress developers and agencies. Users receive a 48-hour early warning for new vulnerabilities and real-time vPatching to protect the applications until the vulnerabilities are resolved.
Patchstack is a globally trusted security partner for many of the leading WordPress hosting companies. We provide a vulnerability notification & mitigation system to the leading WordPress hosting providers such as GoDaddy, Hostinger, Cloudways and many others. If you’re a hosting company, get a free security report here.
Patchstack also provides a free managed vulnerability disclosure program (mVDP) for WordPress plugin & theme makers, helping open-source developers streamline the vulnerability reporting and disclosure process.
Ultimately, Patchstack is on a mission to cover the complete lifecycle of open-source security and is backed by the European Innovation Council, is a member of the Open Source Security Foundation, and in 2024 was selected to join the Google for Startups Growth Academy: AI for Cybersecurity program.


 Essential Addons for Elementor
 WP Fastest Cache
 Gravity Forms
 Fusion Builder
 Flatsome (Theme)
 WP Statistics
 Forminator
 WPvivid Backup and Migration
 JetElements For Elementor